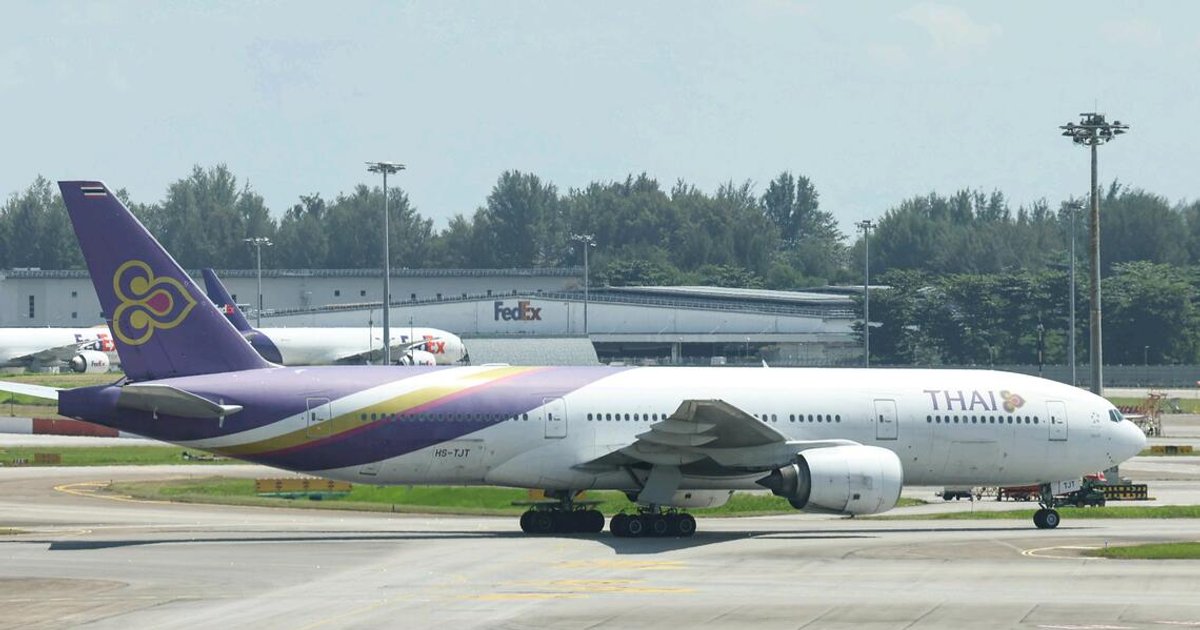
BANGKOK - Thailand’s Transport Ministry has instructed the country’s aviation agencies and service providers holding personal data to strengthen cyber security after Thai Airways disclosed on Nov 9 that about 60,529 passenger booking records may have been accessed without authorisation through its supplier’s system.
Thai Airways confirmed that the incident did not affect its own systems or operations, or passengers’ credit card information. The disclosure comes amid reports of similar incidents involving airlines across Asia that use travel technology provider Amadeus.
Thailand’s Deputy Transport Minister Siripong Angkasakulkiat instructed agencies involved in aviation, along with service businesses maintaining public databases, to tighten security, change access passwords regularly and avoid passwords that could be easily guessed.
“Although the Thai Airways incident involved an attack on a private company’s system, the Transport Ministry has instructed all agencies to tighten protection of stored public data,” he said. “Agencies have also been ordered to strengthen security around access credentials and adopt technology to detect wrongdoing.”
Siripong said that Thailand’s National Cyber Security Agency (NCSA) was monitoring threats and working to prevent malicious access. Government measures also covered investigations and legal action against people who unlawfully accessed personal information.
The Ministry of Digital Economy and Society had described the wider cyber incidents as unprecedented in scale.