📰 Newspapers

Binance chief acknowledges hack ‘shouldn’t have happened’

Binance chief acknowledges hack ‘shouldn’t have happened’

Richard Teng also said at Semafor’s Silicon Valley & The World that the company had previously underinvested in compliance.

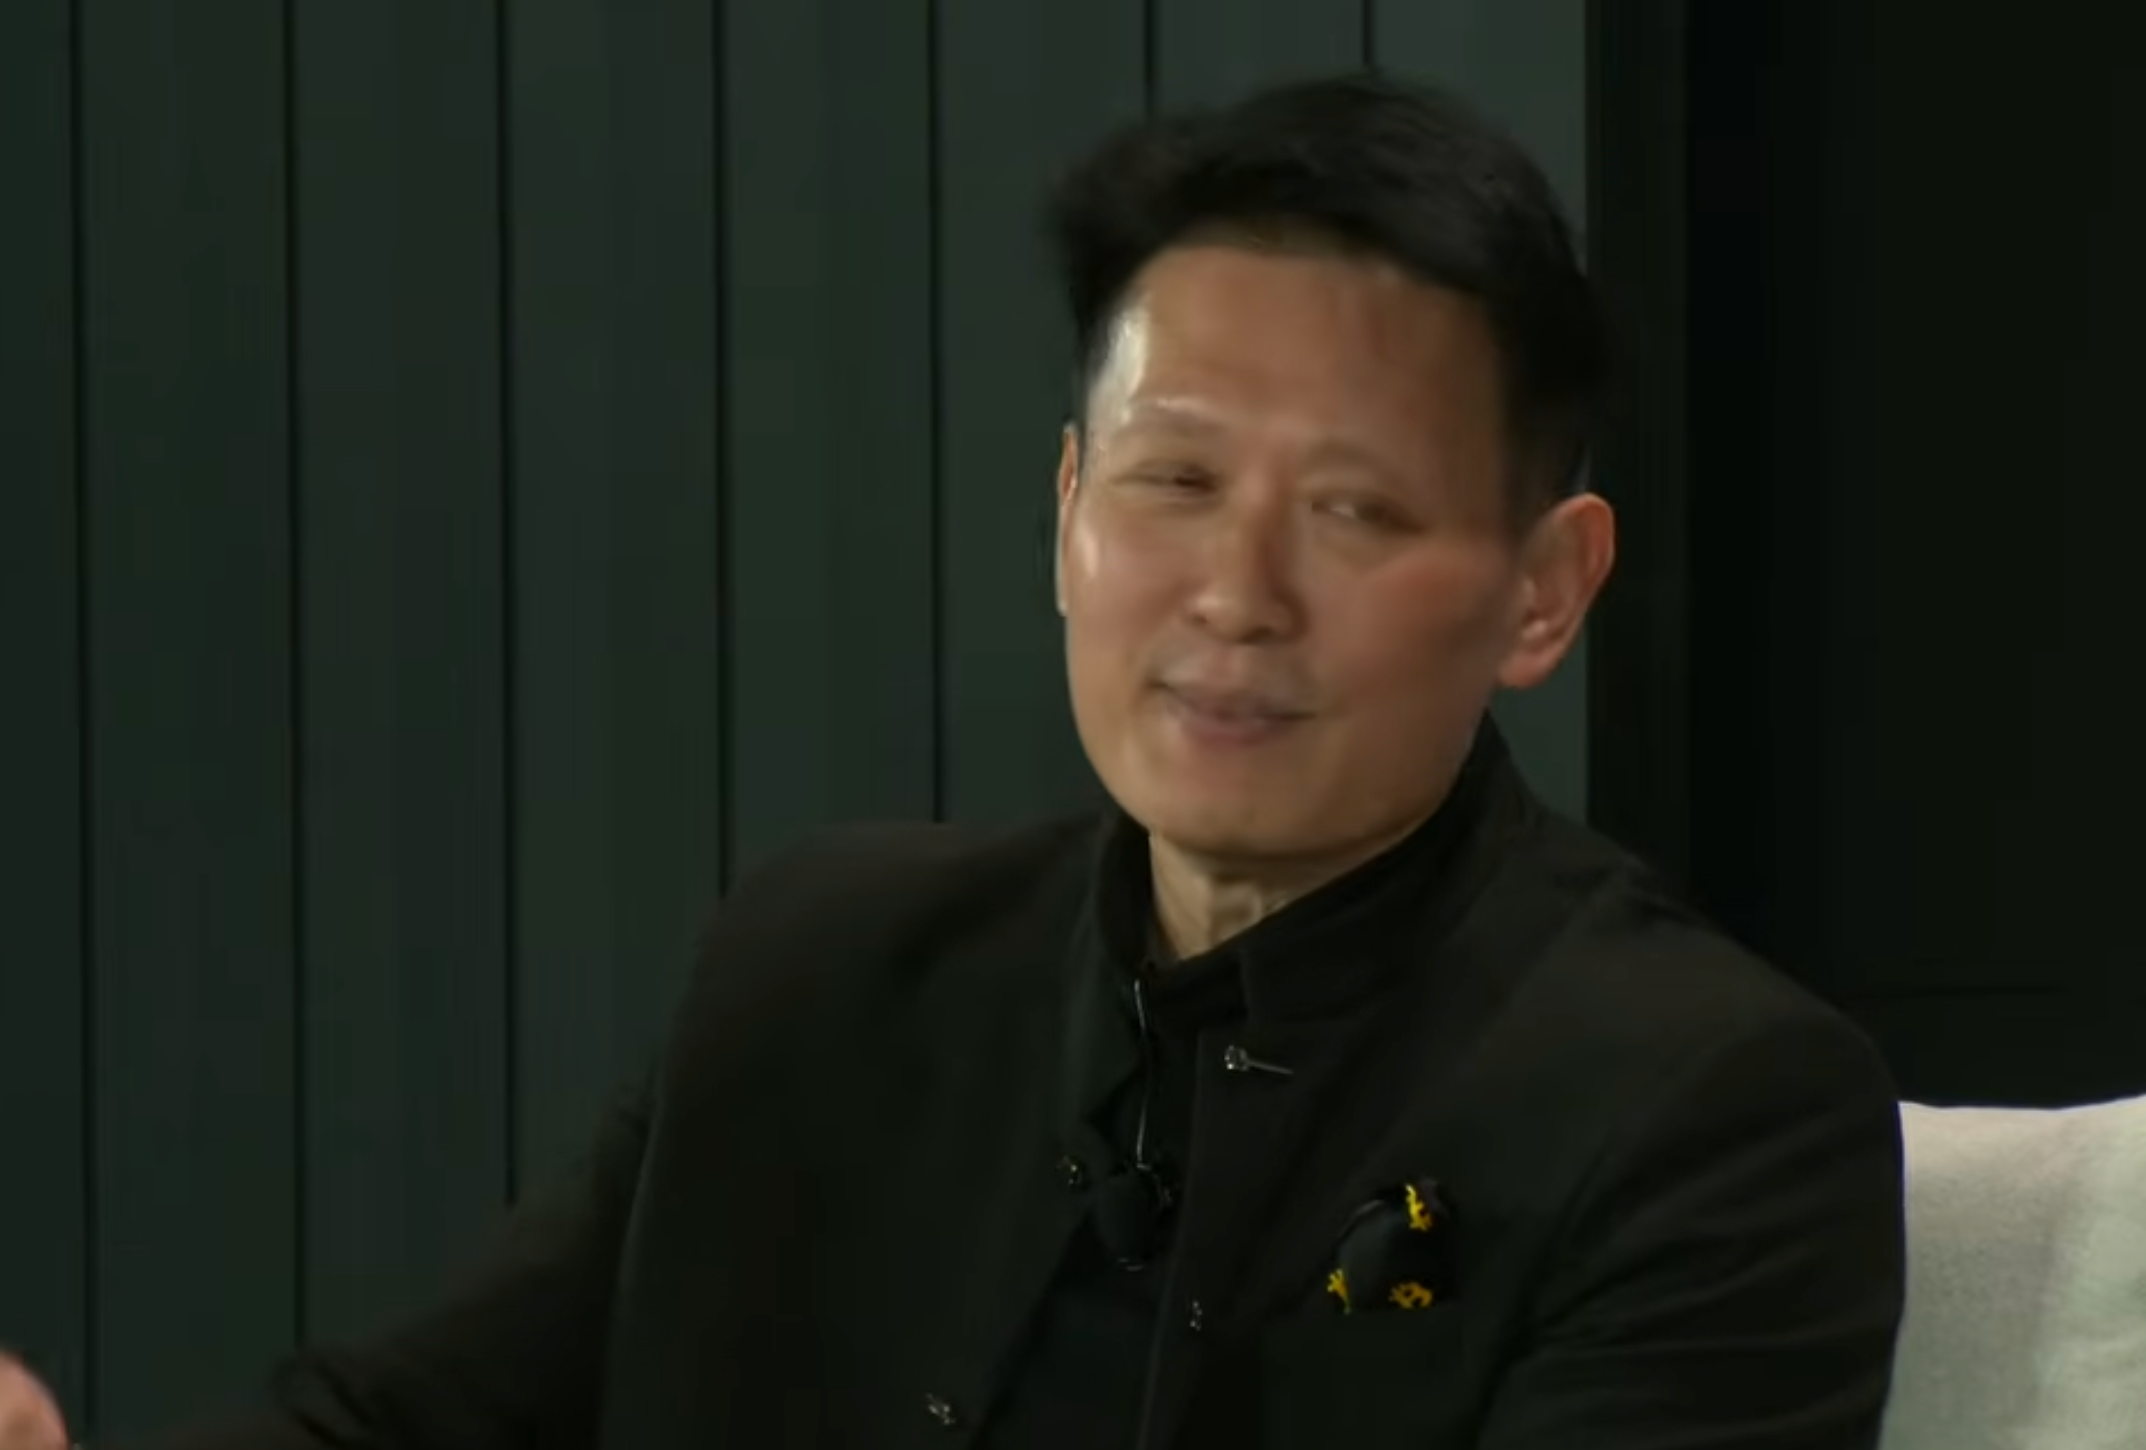
Binance CEO Richard Teng acknowledged Monday that the $6.3 billion hack his firm suffered — one which roiled cryptocurrency markets and raised existential questions about industry security — resulted from the company’s own failings.

“It shouldn’t have happened,” Teng said, speaking at Semafor’s Silicon Valley & The World. “This was a multi-month, sophisticated campaign,” he continued, referring to the attack, which the FBI has attributed to North Korea. (Pyongyang has denied involvement in the hack.)

The hack raised questions about what is fundamentally the weakest link in most cybersecurity and business operations: humans themselves. Binance said that it was compromised in part because of a sophisticated phishing attempt that involved a Binance employee undergoing a fictitious interview process that resulted in “malicious software” being loaded onto a corporate machine, Teng noted.

Teng also acknowledged Binance’s checkered reputation, involving billions in fines for anti-money laundering violations and the imprisonment of its primary shareholder and founder Changpeng Zhao. “We had really underinvested into the area of compliance,” Teng said. “Since the record fine and settlement, we have really invested a great deal.”

Whether that investment is enough is an open question: The New York Times reported in September that Chinese firms continue to use Binance to launder illicit proceeds for the Iranian government.

In brief

Binance CEO Richard Teng acknowledged Monday that the $6.3 billion hack his firm suffered — one which roiled cryptocurrency markets and raised existential questions about industry security — resulted from the company’s own failings. Binance said that it was compromised in part because of a sophisticated phishing attempt that involved a Binance employee undergoing a fictitious interview process that resulted in “malicious software” being loaded onto a corporate machine, Teng noted.

This is the opening of the story, shared with credit to Semafor. The rest of the report — with every detail — continues on the publisher’s website.

Continue reading at Semafor ↗

Cookie settings

Choose which cookies we may use. You can change this at any time from Cookie settings in the footer. Details of each cookie are in the Cookie Policy.

Strictly necessary

Needed for sign-in, security, payments and remembering these choices. Always on.

Preferences

Remember settings such as dark mode.

Analytics & performance

Help us count visits, understand which pages, devices and countries our readers use, and measure how well the site performs – anonymous and aggregated.

Advertising & marketing

Lets advertising partners show and personalise adverts, measure impressions, clicks and visits, prevent ad fraud and pay us – this is how the free site is funded.

🔔 News notifications

Get headlines from NewsHub on this device — even when the site is closed.

You can switch this off at any time. Works on Android, Windows, Mac and Linux browsers; on iPhone/iPad add the site to your Home Screen first.